Email Security Services in Dubai, UAE
Help your team recognise and handle harmful messages while protecting the way your business sends email. Quest Middle East provides email security services in Dubai and across the UAE, covering threat protection, domain authentication, outbound controls and awareness.
- Built in Dubai for the world
- Email and domain protection
- Practical user awareness
Protect the Conversation Behind Everyday Business
Email carries invoices, approvals, customer information and password recovery links. A convincing message can exploit a normal business process without using obvious malware. Protection therefore needs to consider the platform, the sender domain and the decisions people make after a message arrives.
Our email security services review those layers together. We assess your mail environment and legitimate senders, define useful controls and establish a way to report and investigate suspicious messages without losing genuine business communication.
Email Threat Protection: Phishing, BEC and Malicious Attachments
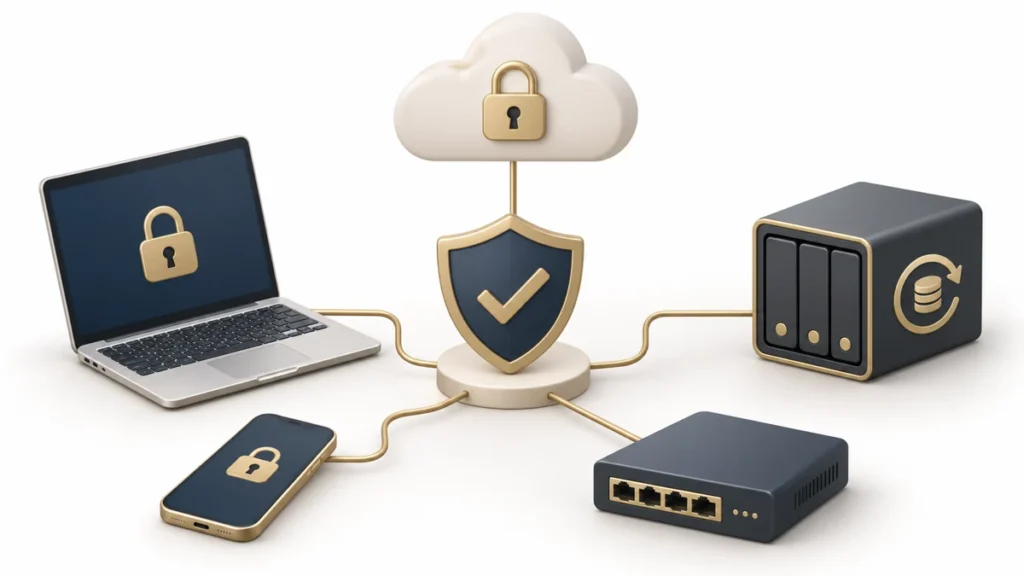
Email threat protection can filter suspicious senders, links and attachments according to the selected platform and licence. Business Email Compromise also needs attention to impersonation, unusual requests and account activity, because a harmful message may look like ordinary correspondence.
We review your current protection, user groups and handling of blocked or quarantined mail. Policies are tested against legitimate workflows, including external partners and automated applications. Alerts and user reports need an owner who can investigate and coordinate the next action.
Reduce Harmful Messages
Review supported anti-phishing, malware and impersonation controls. Identify trusted relationships carefully instead of allowing a broad bypass that weakens protection.
Make Reporting Useful
Give staff a clear reporting route. Define what the reviewer should check and when a concern needs account investigation or escalation into the wider incident process.
SPF, DKIM, DMARC & Domain Protection
Domain authentication helps receiving systems assess whether a message is authorised to use your domain. SPF identifies permitted sending infrastructure; DKIM provides a signature that receivers can validate; DMARC uses alignment and policy to help receivers handle messages that fail the relevant checks.
Configuration starts with an inventory of legitimate senders, not simply adding a restrictive record. Business mail, marketing platforms, invoicing tools and other applications may all send on your behalf. We review the available reports and align the policy with the verified sending environment before proposing stronger enforcement.
Discover Legitimate Senders
List the platforms and suppliers using your domains. Confirm ownership and the changes each sender can support before modifying policy.
Monitor and Progress the Policy
Use reporting and validation to identify failures and unintended impact. Moving toward quarantine or reject should follow a controlled review of authorised senders.
Protect Domain Administration
Review registrar and DNS access, recovery contacts and administrative authentication. Changes to these accounts can affect email and other business services.
Keep Records Current
Add or remove senders as applications and suppliers change. Authentication settings need an ongoing owner rather than a one-time DNS change.
Brand & Digital Asset Protection
Lookalike domains and fake profiles can be used to impersonate your business outside the mail platform you control. Digital asset protection can include a defined monitoring scope, validation of suspected impersonation and coordination of reports to the relevant platform or provider.
We distinguish technical impersonation handling from trademark or legal representation. A takedown request depends on evidence, provider policy and the responsible authority; it is not a guarantee that every suspected asset can be removed immediately. Agree the assets, review process and escalation route before monitoring begins.
Encryption & Outbound Controls
Sensitive business information may need additional controls when it leaves the organisation. Supported email encryption, data loss prevention and outbound policies can help apply the handling rules your business defines. The available functions depend on the platform, licence and recipient experience.
We review the information categories, recipient workflows and exceptions before introducing enforcement. Staff need to understand how to send an approved protected message, how recipients access it and who resolves a legitimate delivery problem. Outbound controls should support an agreed process rather than simply block broad categories of work.
Phishing Awareness and Safer Business Processes
Awareness works best when it connects to decisions staff actually make. Payment changes, unexpected account prompts, requests for confidential information and unusual urgency should have a practical verification route. Training should explain what to do next, not only ask people to spot mistakes in a message.
A scoped awareness programme can include role-relevant guidance, reporting practice and approved simulations where appropriate. The results should guide improvement rather than create blame. Finance, HR, administrators and other roles may need different examples because the requests they receive are different.
Verify Important Requests
Define an independent confirmation process for sensitive changes, such as new bank details. The process should still work when a message appears to come from a familiar person.
Learn From Reports
Review genuine reports and agreed exercises for recurring confusion. Improve the wording, reporting route and workflow as well as the technology.
Integrate With Your Mail and Security Environment
Microsoft 365, Google Workspace and specialist email security products are examples of environments to assess. Existing licences, mail routing, domains, applications and supplier relationships determine the changes that are practical.
Where included, email findings can be connected with endpoint and managed SOC investigation. A suspicious message, unusual sign-in and device alert may need a coordinated review. We agree who owns the mail platform, the domain records and the incident response so the handover is clear.
A Managed Email Security Routine
Assess
Review domains, senders, mail flow, policies and the business processes most exposed to impersonation. Define the services and users in scope.
Introduce Controls
Plan platform and DNS changes, pilot them and validate normal sending and receiving. Agree how quarantined messages and policy exceptions are reviewed.
Operate and Review
Review alerts, authentication reports, reported messages and unresolved actions. Update the sender inventory and policies as the business changes.
Define the Cost
The quote considers users, mailboxes, domains, products, monitoring and awareness activities. DNS work, ongoing protection and incident cleanup are identified in the service scope.
Work With a Team That Understands the Whole Environment
Start With the Business Need
We confirm the systems involved, the concern you want to address and the business processes that depend on them. Recommendations should be understandable to the people who approve the work.
Define Responsibilities
The proposal names covered activities, access, operating hours, escalation and exclusions. Your IT team, application developers and other suppliers can retain clear responsibilities.
Plan Changes and Validation
Agree the implementation, approvals and acceptance checks. Changes to important services need consideration of dependencies, timing and recovery options.
Keep the Service Current
Review outstanding actions and changes in your environment. The right operating routine develops as users, applications and risks change.
Related Security Services
Email Security Services: Your Questions Answered
What do email security services cover?
The scope can include phishing and malware protection, business email compromise controls, domain authentication, digital impersonation monitoring, encryption, outbound controls and awareness. Platforms, users and responsibilities are agreed in the proposal.
What is the difference between SPF, DKIM and DMARC?
SPF identifies permitted sending infrastructure, DKIM provides a verifiable message signature and DMARC applies alignment and policy around authentication results. A safe implementation starts with the legitimate senders using your domains.
Should we set DMARC to reject immediately?
A restrictive policy introduced without understanding legitimate senders can affect genuine mail. Review authentication results, sender support and business impact before progressing enforcement. The appropriate rollout depends on the environment.
Can you stop every phishing message?
No email control can guarantee that every harmful request is blocked. Filtering, authentication, account security, awareness and verification processes work together to reduce the risk.
Can you remove fake domains or profiles?
We can scope validation and reporting of suspected impersonation. Removal depends on evidence, the platform or provider and its policies. Technical reporting is distinct from legal representation.
Will email protection delay genuine messages?
Filtering or authentication changes can affect mail delivery if poorly scoped. We validate legitimate workflows, review quarantines and keep an exception process with an owner.
Can this work with Microsoft 365 or Google Workspace?
The current platform, licences, routing and domains are assessed before confirming integration. Available controls and operating responsibilities vary by product and configuration.
How is the service priced?
User and mailbox counts, domains, licences, authentication work, monitoring and awareness coverage influence cost. Share your mail platform and approximate size for a tailored scope.
Get in touch
Tell us about your environment, the concern you want to address and the support you need. Please do not send passwords, private keys or sensitive incident evidence.