Cloud Security Services in Dubai, UAE
Protect cloud workloads, applications and identities with controls that fit how your business operates. Quest Middle East provides cloud security services in Dubai and across the UAE, covering cloud posture, web application protection and identity and access management.
- Built in Dubai for the world
- Cloud and identity security
- Practical access controls
Make Cloud Access and Exposure Easier to Understand
Cloud platforms make it easy to add a resource, connect an application or invite another user. Those decisions also create permissions, public exposure and dependencies that need to be managed over time. A service can be running well while its security settings deserve attention.
Our cloud security services review the agreed workloads and access paths, prioritise practical improvements and coordinate changes with the people who operate the applications. We work with your existing cloud and development teams so protection is part of the operating process.
Cloud Security Posture & Hardening: AWS, Azure and Google Cloud
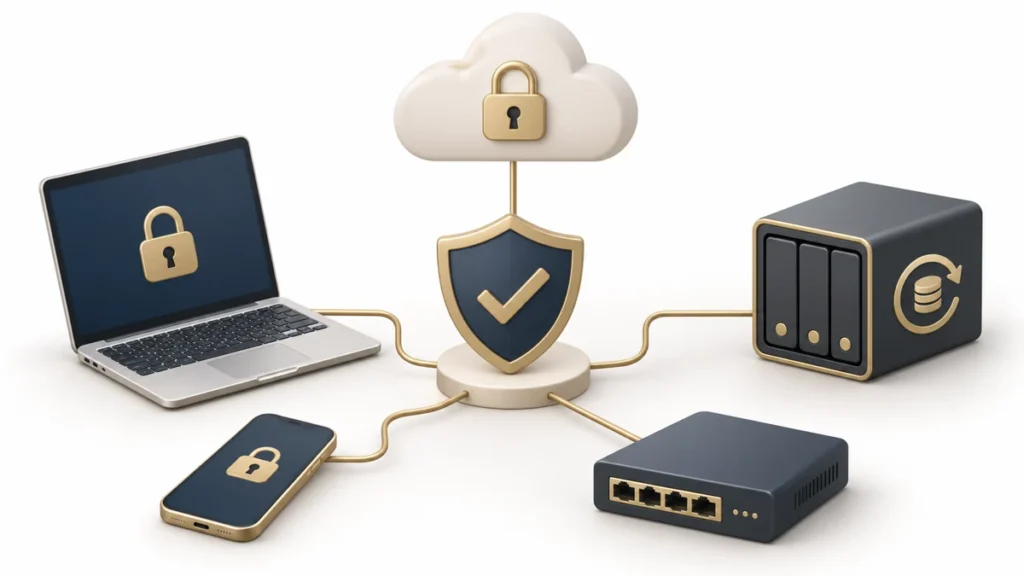
A posture review examines the configuration and exposure of the cloud services within scope. We identify the accounts, subscriptions or projects involved, then review the controls relevant to those workloads, such as administrative access, public endpoints, storage permissions and logging.
AWS, Microsoft Azure and Google Cloud each have different services and responsibility boundaries. Recommendations should fit the actual architecture and selected services, rather than apply a generic checklist without considering application requirements. Changes are prioritised and validated with the workload owner.
Understand the Baseline
Record important resources, owners and dependencies. Identify how configuration is maintained and which settings are enforced through policy or infrastructure code.
Address the Exposure
Review unnecessary access, public services and configuration exceptions. Agree the action, validation and business approval needed for each change.
Web Application Security: WAF, DDoS, Bot and API Protection
Internet-facing applications need protection that understands how they are used. A Web Application Firewall can inspect and control supported web traffic, while other platform functions may address DDoS activity, automated bots or API-specific risks. The exact capabilities depend on the product and deployment.
We review the application entry points, traffic paths and normal requests before scoping controls. Rules are tested and tuned with developers so legitimate sign-ins, uploads, payments and integrations are not unintentionally blocked. Application code vulnerabilities remain a development responsibility unless separately included.
Web and API Entry Points
Identify the hostnames, routes and services in scope, together with certificate, proxy and origin dependencies. Decide which traffic should reach the application and how exceptions are reviewed.
Operating the Protection
Agree rule ownership, logging, alert handling and change validation. Review false positives and new application behaviour as releases and usage change.
Identity & Access Management: SSO, MFA and PAM
Identity is a central part of cloud security because an authorised account can still have more access than its role requires. Identity and Access Management brings account lifecycle, authentication and permissions into a documented process.
Single Sign-On can simplify access across supported applications; Multi-Factor Authentication adds another verification step; Privileged Access Management addresses elevated access and its oversight. We assess your identity provider, application compatibility and licence coverage before confirming which functions can be delivered.
Joiners, Movers and Leavers
Define how access is granted, changed and removed as people and suppliers change roles. Keep an owner for service accounts and other identities that do not belong to an individual employee.
Privileged Access
Review administrative roles, emergency access and the process for approved elevated work. Where supported, consider time-limited access and records that show how privileged actions are authorised.
Authentication and Recovery
Plan MFA enrollment, recovery and exceptional access. Stronger sign-in controls need a practical support process so a lost device does not become an uncontrolled bypass.
Access Reviews
Give resource owners a usable view of permissions and exceptions. Review access against current responsibilities rather than simply renewing every historic grant.
Zero Trust Planning
Zero Trust is an architectural approach to access decisions, not a product that can be installed once. A practical plan considers the user, device, resource and context of a request, alongside the permissions needed to perform the work.
We help identify realistic steps around identity, device conditions, application access and segmentation. Begin with the services and users where a change will reduce a defined risk, then test the effect on normal workflows. Existing dependencies and recovery access must remain understood throughout the rollout.
Security Across Cloud and Development Workflows
A cloud configuration change, new application release or supplier integration can alter exposure. Security needs a route into the way those changes are designed and approved. We identify the responsibilities of cloud operations, developers, identity owners and security staff so findings reach the right team.
Cloud security is distinct from general resource administration and application delivery. Connect the security scope with managed cloud services and DevOps where you also need ongoing infrastructure operation or repeatable deployment processes.
Monitoring, Evidence and UAE Requirements
Agree which security and access events are needed for the selected controls, how long they are kept and who reviews them. Connect those sources with managed SOC coverage where you need an ongoing investigation and response workflow.
For UAE organisations, storage location, access and retention should be checked against the requirements confirmed by your responsible team. Technical work can support applicable UAE IAS/NESA, DESC, data protection or sector controls, but the cloud platform and service scope must be assessed rather than assuming every workload has identical obligations.
A Cloud Security Engagement With Clear Outputs
Review and Prioritise
Agree the accounts, workloads and identities in scope. Record findings with their business relevance, dependencies and recommended next action.
Plan and Validate
Coordinate changes with the owners of applications and access. Check important workflows and retain rollback considerations where practical.
Operate and Review
Define monitoring, maintenance, exception handling and reporting for ongoing coverage. Keep the inventory and access model current as workloads change.
Quote Against the Environment
The proposal considers cloud footprint, identity platforms, applications, licences and operating coverage. One-time improvement work and managed operations are scoped separately.
Work With a Team That Understands the Whole Environment
Start With the Business Need
We confirm the systems involved, the concern you want to address and the business processes that depend on them. Recommendations should be understandable to the people who approve the work.
Define Responsibilities
The proposal names covered activities, access, operating hours, escalation and exclusions. Your IT team, application developers and other suppliers can retain clear responsibilities.
Plan Changes and Validation
Agree the implementation, approvals and acceptance checks. Changes to important services need consideration of dependencies, timing and recovery options.
Keep the Service Current
Review outstanding actions and changes in your environment. The right operating routine develops as users, applications and risks change.
Cloud Security Services: Your Questions Answered
What do cloud security services include?
Cloud security can include posture review, hardening, web application protection, identity and access management and ongoing monitoring. The accounts, services, users and operational responsibilities included are agreed after discovery.
Do you work with AWS, Azure and Google Cloud?
We assess the platforms and workloads in your environment, including AWS, Microsoft Azure and Google Cloud. Supported functions, access, licences and the responsibility boundaries of each service are confirmed before work is scoped.
Is a WAF enough to secure our website?
No single control covers every risk. A WAF addresses supported web traffic controls; application code, identity, hosting configuration, updates, backups and monitoring also need appropriate owners.
Can you help with SSO, MFA and privileged access?
These can be included where supported by your identity provider, applications and licences. We review compatibility, enrollment, recovery and administrative access before confirming a design.
Will security changes affect our applications?
They can, especially when access or traffic controls change. We plan with the application owner, test important workflows and agree the timing and validation of changes.
Is Zero Trust a product?
It is an architectural approach to access and trust decisions. Products may support parts of it, but the design also depends on identity, devices, applications and operating procedures.
Can logs and data remain in the UAE?
Location depends on the selected platform, region, product and service design. Storage, access, retention and supplier arrangements are confirmed against your stated requirements.
How much does cloud security cost?
Cost depends on workloads, accounts, identity systems, applications, licences and the operating coverage needed. Share a short inventory and your priorities for a tailored proposal.
Get in touch
Tell us about your environment, the concern you want to address and the support you need. Please do not send passwords, private keys or sensitive incident evidence.